Lead analysis · October 6, 2026
The SEC Asked Whether an AI Agent Can Sign the Transfer
The Securities and Exchange Commission published a proposed rule in the Federal Register on October 6, 2026, covering how investment advisers and regulated funds may custody certain crypto assets under federal law. The 234-page document (File S7-2026-35, 91 FR 63870) sets out specific requirements for private-key management, joint authorization, and client-asset segregation, and it includes a request for public comment that asks a pointed institutional question: are advisers or custodians currently using non-human software agents, including automated smart contracts and artificial intelligence, as signatories on crypto transactions, and should those arrangements be expressly permitted or prohibited? Comments are due December 7, 2026.
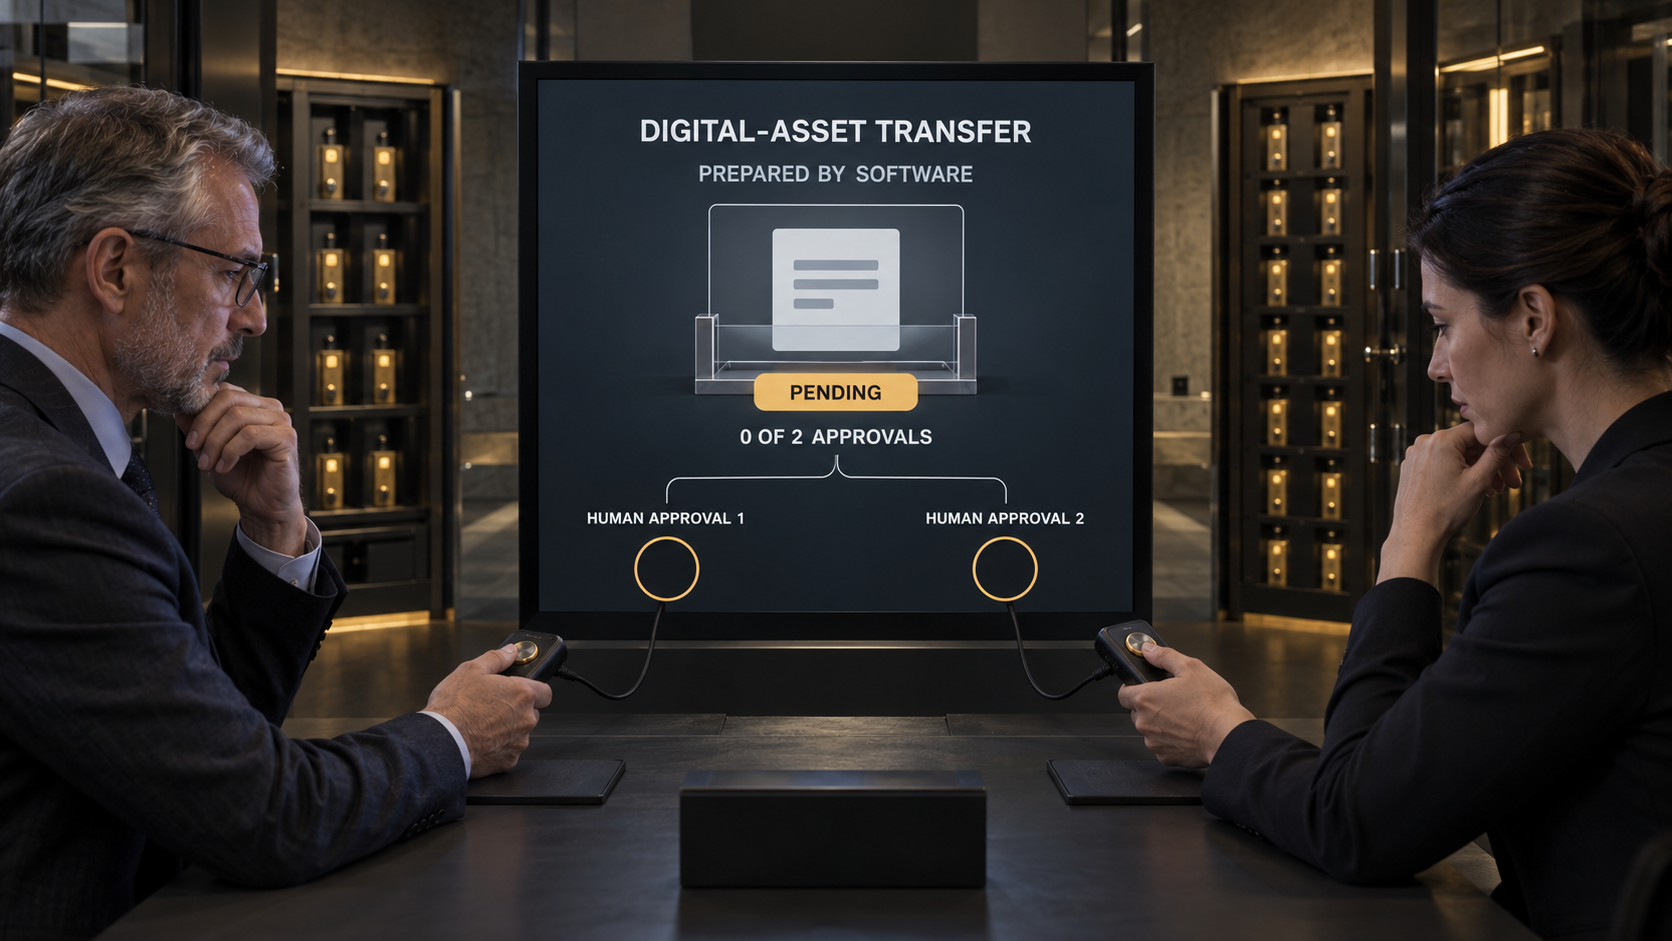
That question is not a grant of authority. The proposal itself requires that covered crypto transactions be jointly authorized by at least two designated persons, that at least one of those persons be a management person, and that the management person for a regulated fund also hold officer status. The agency is soliciting evidence about existing practice and asking the public to weigh in on whether software-agent signatories enhance or undermine safeguarding.
This wider proposal has a carefully bounded scope. As Commissioner Hester Peirce noted in her accompanying statement, the self-custody path the rule creates for advisers is available only in limited circumstances when no permitted custodian can be found. An adviser pursuing that path must make the determination in writing at the outset and again every quarter. That initial determination carries obligations including custody-specific expertise and systems, cybersecurity controls, annual reviews, independent internal control reports, quarterly account statements that identify addresses and networks, and client-asset segregation by address so clients can compare the adviser's records against onchain activity.
The proposal treats joint authorization as one safeguard among several against an irreversible transfer. It also discusses multisignature or multiparty controls, identity checks, transaction simulation, approved destinations, and revocation. Software already participates in many of those steps. An agent can assemble a transaction, apply policy, check a destination against an allowlist, simulate execution, and present the result to a human approver. Permitting that same agent to become a signatory moves it from preparation into authorization authority.
That distinction matters because a cryptographic signature answers a limited question: did the holder of this credential authorize these transaction bytes at this moment? It does not establish that the transfer matched a client instruction, stayed within a documented risk limit, went to the intended counterparty, or received independent human scrutiny before execution. If two automated signers share the same model, data feed, policy engine, key infrastructure, or administrator account, both signatures may still represent a single failure path rather than two independent checks. The protective value of two approvals depends on the authorizing principals being separate.
Verification bottleneck
Rule status. This is a proposed rule open for comment through December 7, 2026. It does not currently permit software agents as signatories, and it does not govern all crypto custody, only specific covered crypto assets held by regulated advisers and funds.
Principal identification. A custody system would need to record whether an approval came from a named human, a software agent, or a human acting through an agent, along with the specific delegated authority in effect at that moment.
Independence of principals. Two signatures function as a safeguard only if the authorizing principals and their failure paths are meaningfully separate. Shared infrastructure, shared keys, or a common administrator can collapse two signatures into one.
Receipt completeness. Onchain inclusion confirms that a transfer occurred. A complete record also captures the client instruction, the policy version applied, the destination approval, the simulation result, the management authorization, and the final outcome so that a later review covers the full decision rather than only the cryptographic event.
Key development to monitor. The meaningful threshold will be whether a final rule permits software-agent signatories, prohibits them outright, or permits them under defined conditions such as a mandatory human management gate, key separation, and enhanced logging.
Opportunities
This leaves custody teams time before a final rule to build and test an agent-signature acceptance layer. That layer would assign each signer to a distinct authorization principal, map shared dependencies and failure paths, require a human management gate wherever the proposed rule calls for a management person, simulate every transaction before signing, restrict destinations to an approved list, maintain revocation controls keyed to personnel and account status, and separate key material across systems and roles.
And a receipt would capture the proposed transaction, policy version, each signer's identity and authority, evidence reviewed, simulation result, destination approval, authorization time, network confirmation, and any exception. That record supports both regulatory review and client reconciliation against onchain activity, which the proposal's account-statement requirements anticipate.
The SEC's question in Request for Comment 77 marks a specific institutional threshold. Software agents are now being considered for the authorization layer where a transfer of assets that may be irreversible can be initiated. The design question for institutions is not only whether an agent can hold a signing credential. It is whether the authorization process can preserve independent judgment, accountable human authority at the management level the rule specifies, and a receipt detailed enough to reconstruct every element of the decision.
This article describes a proposed rule and open comment process. It is not legal or investment advice.